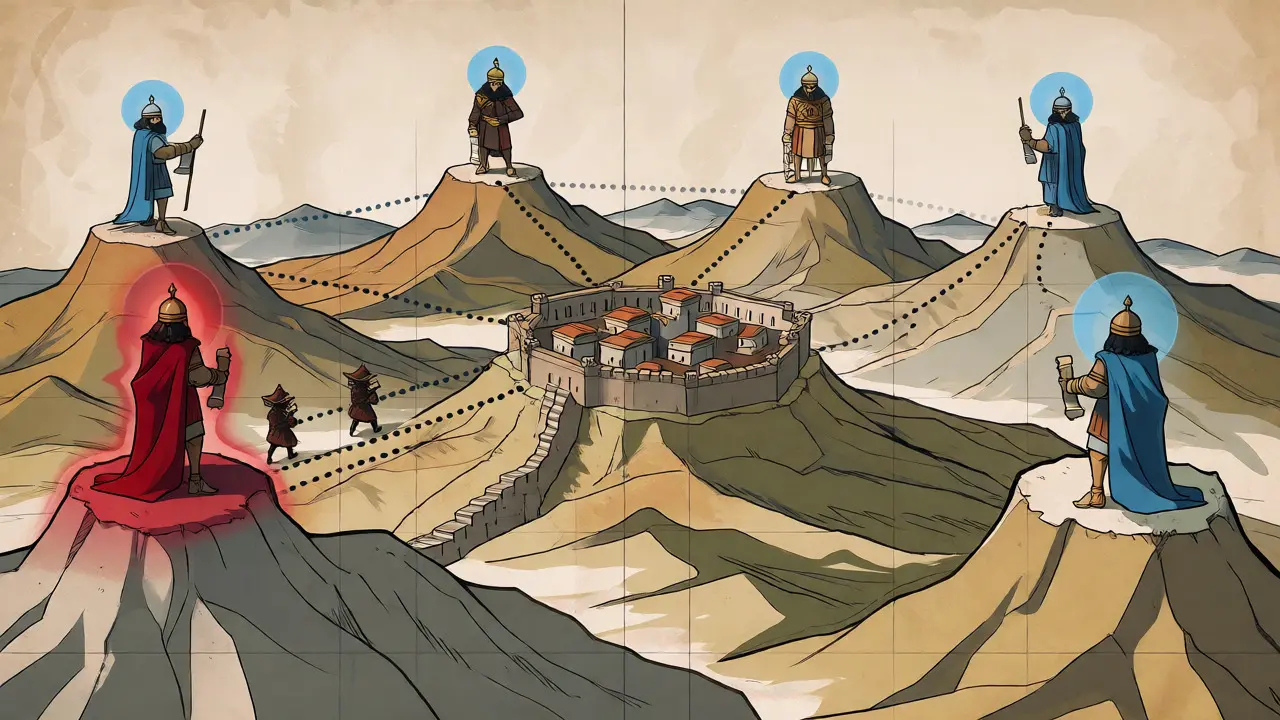
Imagine you’re leading an army in ancient times. You and three other generals surround a city. To win, you must attack at the exact same moment. If one attacks early while others wait, you lose. But here’s the catch: you can’t talk face-to-face. You send messengers through enemy territory. What if some messengers are captured? What if they lie? What if one general is actually a traitor trying to sabotage the whole operation?
This isn’t just a war movie plot. It’s the Byzantine Generals Problem, a fundamental computer science challenge that describes how decentralized networks agree on truth when participants might fail or act maliciously. First described in 1982 by Leslie Lamport, Robert Shostak, and Marshall Pease, this problem is the bedrock of why Bitcoin and Ethereum work. Without solving it, digital money would be easy to fake, and blockchains would collapse into chaos.
Why Trust Is Hard in Distributed Systems
In a centralized system like your bank’s database, there’s one source of truth. If the server says you have $100, you have $100. Easy. But in a distributed system, no single node is trusted. Every computer (node) holds a copy of the data. They need to agree on which transactions are valid. If even one node sends bad info-whether due to a glitch or a hacker-the whole network could split into two different realities. This is called a "fork," and it’s a nightmare for consensus.
The Byzantine Generals Problem formalizes this fear. It asks: How do we ensure all honest nodes reach the same decision, even if some nodes are faulty or actively lying? In computer science terms, these aren’t just crashes where a computer stops working. These are "Byzantine faults," where a node behaves unpredictably, sending conflicting messages to different peers. One peer hears "Attack," another hears "Retreat." Who do you believe?
The Math Behind the Mayhem
Lamport didn’t just pose a riddle; he provided a mathematical proof. For a network to survive Byzantine faults, you need a specific ratio of honest nodes to faulty ones. The golden rule is n > 3f. Here, n is the total number of nodes, and f is the maximum number of faulty nodes allowed.
Let’s break that down. If you want to tolerate one faulty node (f=1), you need at least four nodes total (n=4). Why four? Because if you only had three, and one lied, the remaining two couldn’t reliably determine who was wrong. With four, the three honest nodes can compare notes. Two honest nodes will tell you the truth, outvoting the liar. This threshold ensures that as long as less than one-third of the network is compromised, the honest majority wins.
This differs sharply from simpler problems like Crash Fault Tolerance (CFT). In CFT systems (like traditional databases using Paxos or Raft), nodes either work or they stop. They don’t lie. For CFT, you only need n > 2f+1. So, to handle one crash, you need three nodes. Byzantine Fault Tolerance (BFT) is much harder because it assumes malice, not just accidents. That extra layer of paranoia costs resources.
| System Type | Fault Behavior | Minimum Nodes (for f=1) | Complexity |
|---|---|---|---|
| Crash Fault Tolerance (CFT) | Nodes stop responding | 3 | Low |
| Byzantine Fault Tolerance (BFT) | Nodes lie or act randomly | 4 | High |
How Bitcoin Solved the Riddle
For decades, the Byzantine Generals Problem remained theoretical. Then came Satoshi Nakamoto. Bitcoin didn’t solve BFT in the traditional sense (where every node votes). Instead, it used Proof-of-Work (PoW) to sidestep the issue entirely. Think of PoW as a way to make lying expensive. To add a block, a miner must solve a complex math puzzle. This requires massive energy and hardware. If a miner tries to cheat, they waste that energy. Honest miners follow the longest chain because it represents the most work invested.
Vitalik Buterin, co-founder of Ethereum, noted that Bitcoin was the first practical solution for open networks. It works because economic incentives align with honesty. You don’t need to trust the person sending the message; you trust the math and the cost of deception. However, this solution comes with a heavy price tag: energy consumption. Dr. Andrew Miller from the University of Illinois has pointed out that while PoW solves the problem, it creates new challenges regarding sustainability and scalability.
Ethereum’s Shift to Proof-of-Stake
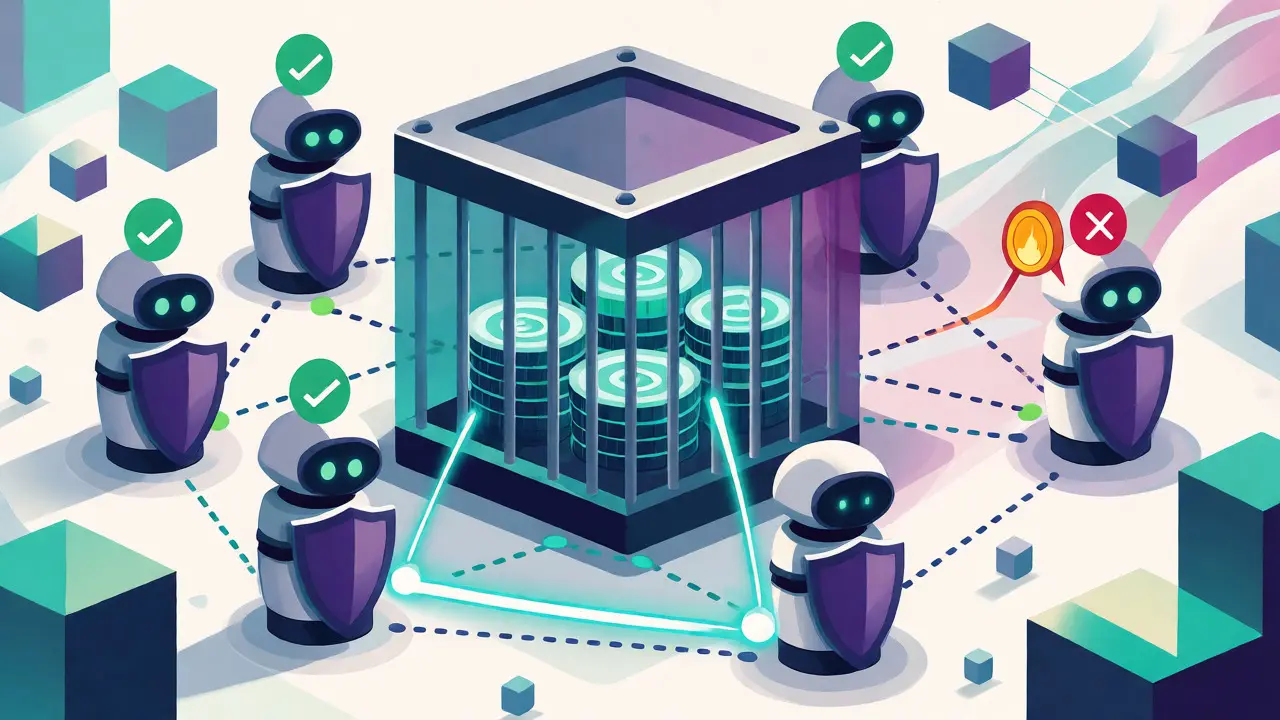
If PoW is paying rent to keep the peace, Proof-of-Stake (PoS) is putting up a deposit. Ethereum’s transition to PoS in 2022 marked a major evolution in handling Byzantine faults. In PoS, validators lock up their own cryptocurrency (ETH) as collateral. If they act dishonestly, they get "slashed"-their stake is burned. This economic penalty replaces the energy burn of PoW.
Ethereum uses a modified BFT approach called LMD-GHOST. It doesn’t require every validator to vote on every block, which keeps things fast. Instead, it relies on checkpoints. As long as more than two-thirds of the staked ETH agrees on a checkpoint, the network moves forward. This reduces energy use by 99.95% compared to PoW. According to Ethereum Foundation metrics, this system maintains high reliability across thousands of nodes. It’s faster, cheaper, and still secure against Byzantine actors, provided the attackers don’t control more than one-third of the total stake.
Practical Challenges for Developers
If you’re building a private blockchain or a enterprise DLT (Distributed Ledger Technology), you’ll likely implement a direct BFT algorithm like Practical Byzantine Fault Tolerance (PBFT) or Tendermint. These algorithms involve multiple rounds of voting. Nodes propose blocks, pre-vote, and then commit. It’s rigorous but slow as the network grows.
Developers often hit walls here. A common pitfall is underestimating the communication overhead. PBFT requires every node to talk to every other node. Message complexity scales quadratically (O(n^2)). Add more nodes, and the chatter becomes deafening. Newer protocols like HotStuff try to fix this by reducing complexity to linear (O(n)), allowing networks to scale to tens of thousands of nodes.
Another hurdle is "liveness." Can the network keep making progress even if some nodes are offline? BFT systems struggle if too many nodes go silent. You need strict timing assumptions. If your internet connection lags, you might look like a faulty node. In real-world deployments, like those seen in financial services trials, tuning these timeouts is critical. A 2022 survey showed that nearly 70% of enterprises needed external consultants to get their BFT implementations right.
Beyond Crypto: Where Else Does This Matter?
You might think this is just for crypto nerds, but BFT is everywhere. NASA uses it for spacecraft controls. If a sensor on a Mars rover gives weird data, the flight computers must decide whether to trust it or ignore it without human intervention. They use BFT logic to prevent a single bad sensor from crashing the mission.
The automotive industry is adopting it too. Self-driving cars communicate with each other (V2V). If one car sends false location data, it could cause a collision. Standards like ISO 21448 require robust fault tolerance. Similarly, the US electrical grid is integrating BFT to manage decentralized power sources. If solar panels report inconsistent output, the grid needs a consensus mechanism to balance load without trusting any single meter blindly.
Key Takeaways
- The Core Issue: Achieving agreement in a network where participants may lie or fail unpredictably.
- The Magic Number: You need more than 2/3rds of nodes to be honest (
n > 3f) to guarantee consensus. - Bitcoin’s Approach: Uses Proof-of-Work to make cheating economically unviable rather than relying on voting.
- Ethereum’s Evolution: Moved to Proof-of-Stake with BFT elements for speed and energy efficiency.
- Real-World Use: Critical for aerospace, autonomous vehicles, and smart grids, not just cryptocurrencies.
What is the main difference between Byzantine faults and crash faults?
Crash faults occur when a node simply stops working or goes offline. Byzantine faults are more dangerous because the node continues to operate but sends incorrect or contradictory information to different parts of the network. It’s the difference between a phone being dead versus a person intentionally lying to you.
Why does the Byzantine Generals Problem require n > 3f?
This formula ensures that the number of honest nodes is sufficient to outvote and identify the faulty ones. If you have f traitors, you need enough loyal generals so that no matter how the traitors spread lies, the loyalists can still form a majority consensus among themselves. Fewer than 3f+1 nodes cannot guarantee this agreement if up to f nodes are malicious.
Does Bitcoin use Byzantine Fault Tolerance directly?
Not in the traditional voting sense. Bitcoin uses Proof-of-Work, which probabilistically solves the Byzantine Generals Problem. It makes it computationally expensive to rewrite history, effectively deterring malicious actors without requiring every node to explicitly vote on every transaction in a BFT-style round.
Can a blockchain function if more than 1/3rd of nodes are faulty?
Generally, no. Most BFT-based blockchains halt or become insecure if faulty nodes exceed 1/3rd of the total network weight or count. This is known as the "safety" limit. Beyond this point, the network cannot distinguish truth from lies reliably, risking forks or double-spending.
Is the Byzantine Generals Problem relevant outside of cryptocurrency?
Yes, absolutely. Any system where independent components must agree without a central controller faces this issue. Examples include aviation control systems, autonomous vehicle fleets, distributed databases, and smart grid management, where sensor failures or cyberattacks mimic Byzantine behavior.
 Finance